Protecting the business in today's cybersecurity climate is all about staying up-to-date. Up-to-date with your security technology, up-to-date with security patches and up-to-date with the tools, techniques and procedures of different threat actors. In this post, we...
Sentinel One News
Category: Sentinel One News
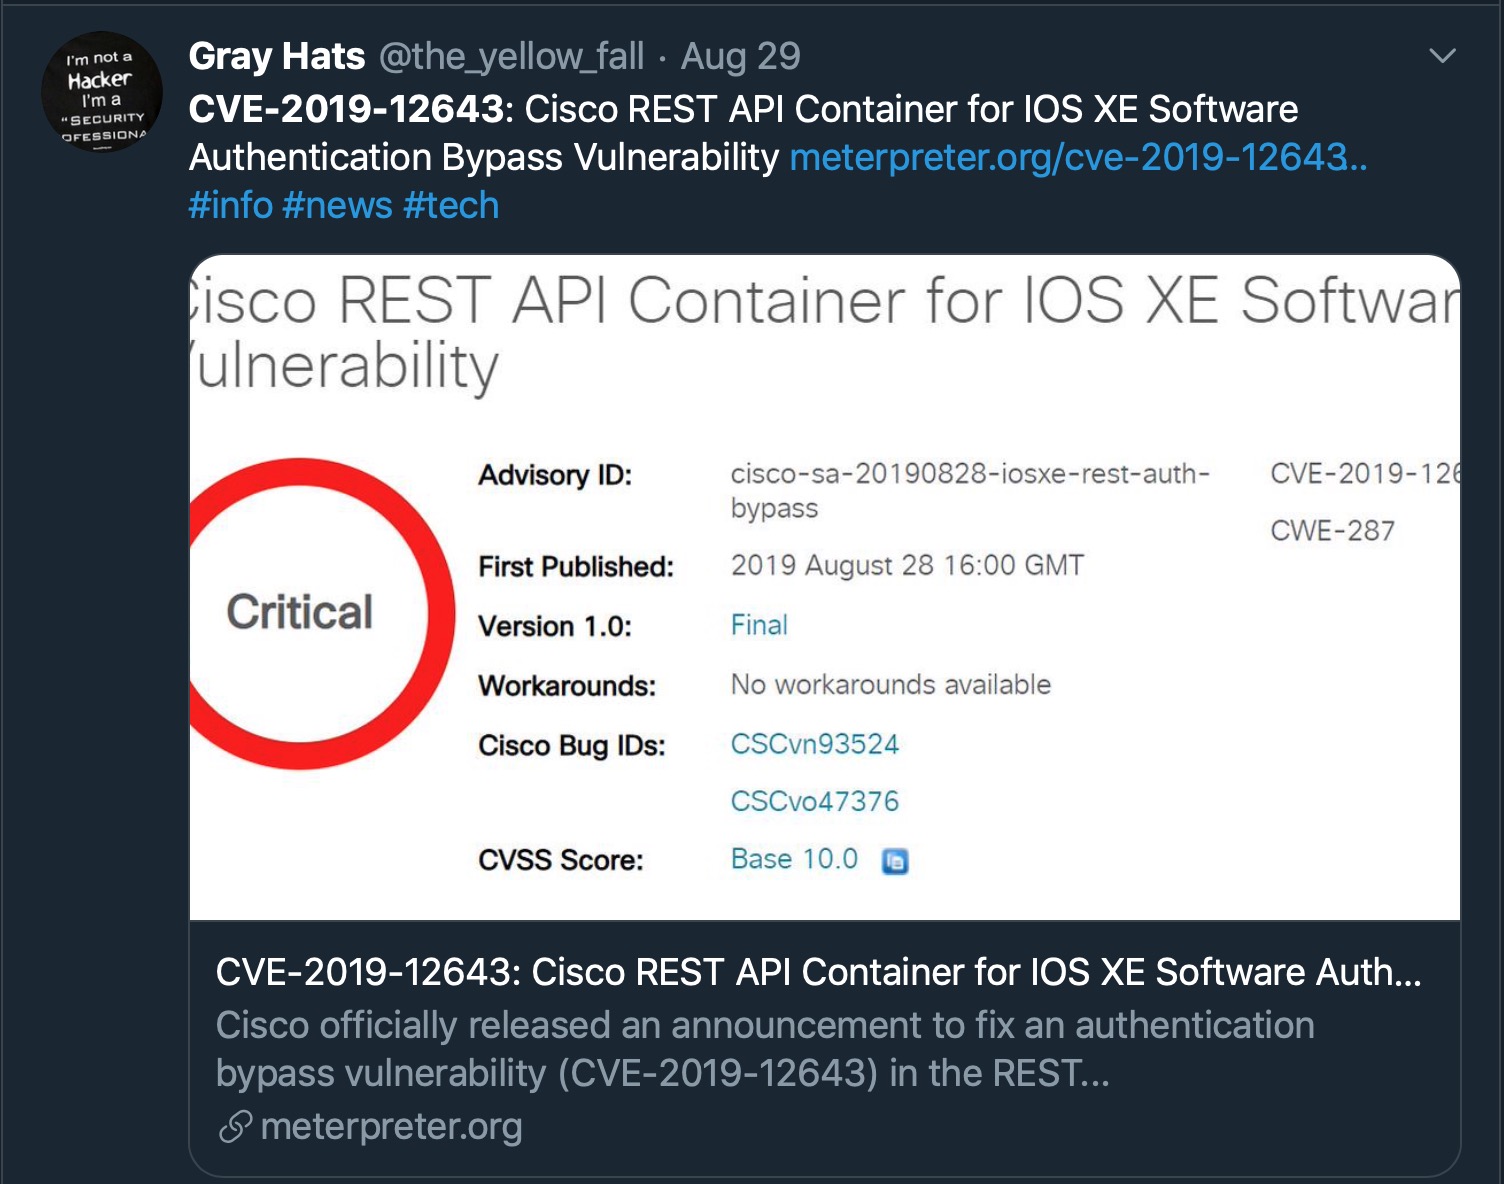
The Good, the Bad and the Ugly in Cybersecurity – Week 36
The Good The hero of the day is the city of New Bedford, Massachusetts. After (another) typical ransomware attack on a US city (this time, using the Ryuk ransomware) and a ransom request of $5.3 million, the city negotiated it down to $400k, and eventually moved on to...
Gootkit Banking Trojan | Part 3: Retrieving the Final Payload
Gootkit's final payload contains multiple Node.js scripts. Join Daniel Bunce as he reverse engineers the malware to take a deeper look at what it delivers. The Gootkit Banking Trojan was discovered back in 2014, and utilizes the Node.js library to perform a range of...
macOS Incident Response | Part 3: System Manipulation
In Part 1 and Part 2, we looked at collecting device, file and system data and how to retrieve data on user activity and behavior. In this final part of the series, we're going to look for evidence of system manipulation that could leave a device or a user vulnerable...
Endpoint Security | Winning the War Against Time
What is the one common denominator against any adversary? What is the most precious commodity of all in the struggle between attackers and defenders? What is the one advantage the adversary has, up till now, always had over us? The answer is time itself. The reason...
The Good, the Bad and the Ugly in Cybersecurity – Week 35
The Good Apple, Microsoft and now Google have all made important announcements about new and extended bug bounty programs recently. This week, Google took their turn in announcing a new program to reward the reporting of data abuse issues in Android apps, Chrome...
Gootkit Banking Trojan | Part 2: Persistence & Other Capabilities
Following on from the previous post, Daniel continues exploring the Gootkit banking trojan, revealing its persistence techniques and other capabilities. The Gootkit Banking Trojan was discovered back in 2014, and utilizes the Node.JS library to perform a range of...
macOS Incident Response | Part 2: User Data, Activity and Behavior
In the previous post in this intro series on macOS Incident Response, we looked at collecting device, file and system data. Today, in the second post we're going to take a look at retrieving data on user activity and behavior. Why Investigate User Behavior? There's a...
Reach Me
Request a Call Back by filling out and submitting the following form.